
A US-based SaaS company can spend months preparing its European launch, only to discover that its privacy notice has no EU contact point, its customer-support team isn’t prepared for authority correspondence, and nobody has documented who will receive a data subject request. The company may have no EU office, no European employees, and no local subsidiary, yet its services can still bring it within the GDPR’s territorial scope.
That gap is where an EUデータ保護代表者 becomes important. Article 27 is not a substitute for GDPR compliance, a local DPO, or an EU establishment. Where a controller or processor is EU域内に設立されていない but is subject to the GDPR under 第3条(2), Article 27 generally requires it to designate a representative in the Union unless an Article 27(2) exemption applies. The role increasingly needs to fit alongside representation or contact-point obligations arising under other European digital laws.
Understanding the EU Data Protection Representative Role
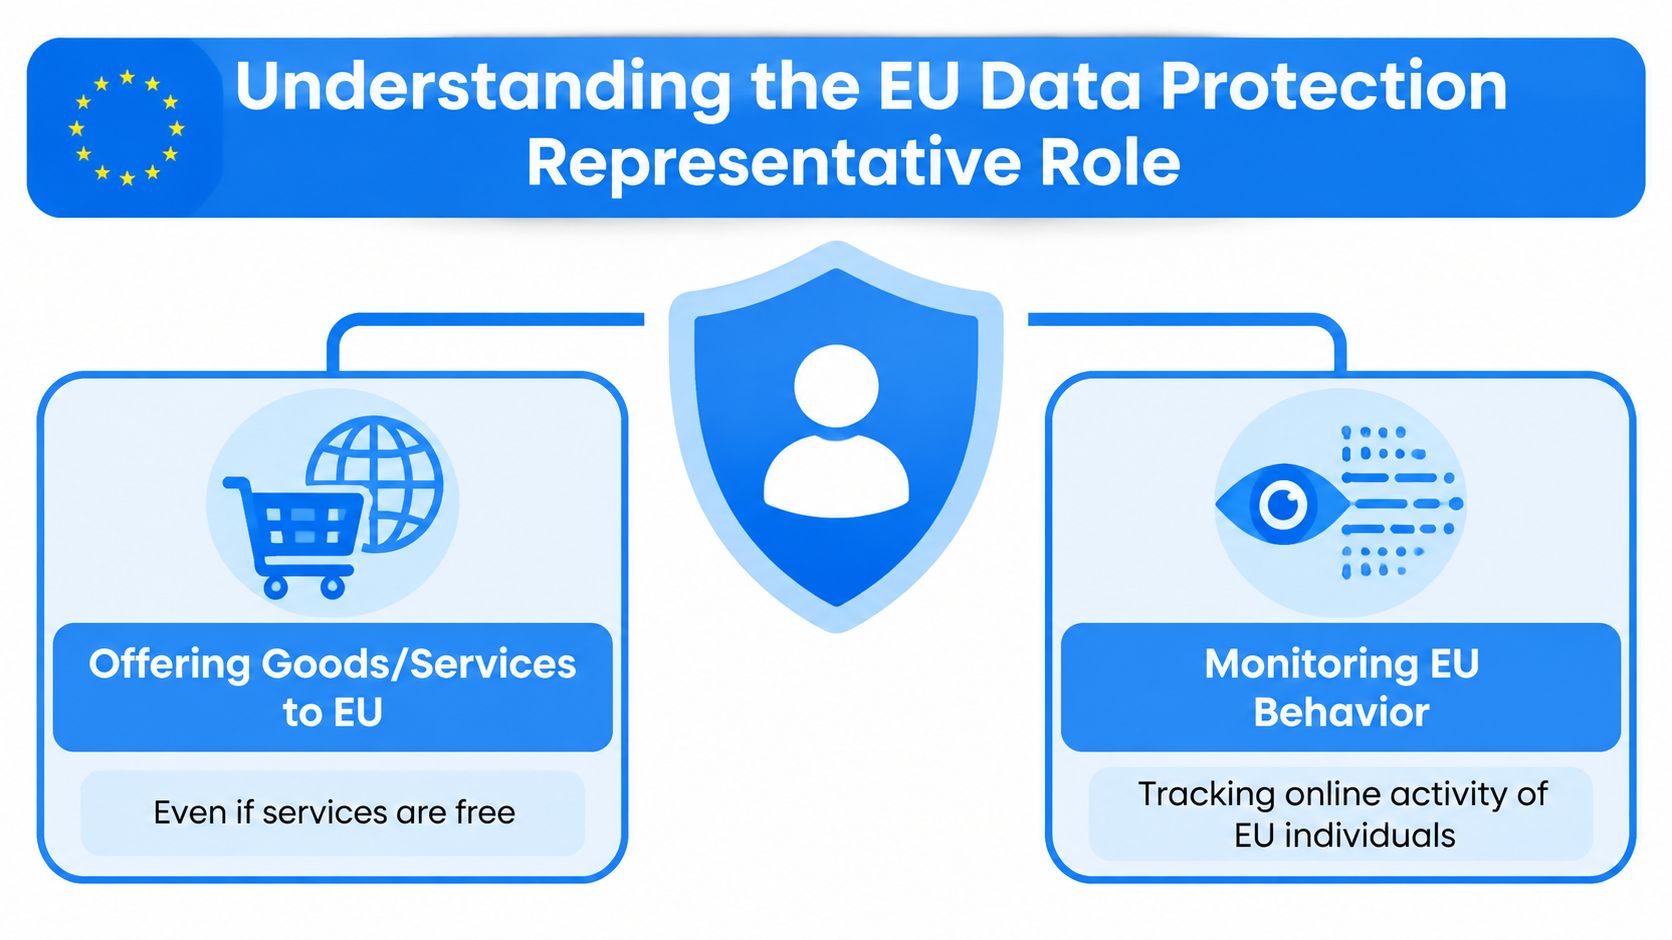
The simplest way to understand the role is to treat it as a registered contact point for GDPR matters in the EU. A non-EU business that is subject to the GDPR under 第3条(2) because it offers goods or services to people in the EU or monitors their behaviour may need an EU representative, unless a narrow exemption applies. The representative must be established in a Member State where the data subjects whose personal data are processed are located, appointed in writing, and mandated to be addressed by supervisory authorities and data subjects on all issues related to processing for the purposes of ensuring compliance with the GDPR. These requirements are set out in GDPR Article 27.
Consider a Canadian analytics platform that begins serving French customers. Its engineers, legal team, and servers may remain outside the EU, but French users still need a practical way to contact the business about how their personal data is processed. A supervisory authority also needs an identifiable representative in the Union that can be addressed on relevant processing matters and coordinate with the organisation responsible for the processing.
A contact point with a statutory mandate, not a substitute decision-maker
An EU data protection representative is not the same as a Data Protection Officer. A DPO advises the organisation, monitors its data protection programme, and performs the functions assigned to that role under the GDPR. The representative, by contrast, acts as an in-market contact for authorities and data subjects under a specific statutory mandate. A business can need both, and appointing one does not automatically satisfy the other role. The EDPB has also taken the position that the Article 27 representative role is incompatible with acting as the external DPO for the same organisation, because the DPO must be able to act independently and avoid conflicts of interest.
The representative is not simply a consultant who reviews cookie banners or rewrites a privacy policy. It may receive communications, facilitate engagement with supervisory authorities and data subjects, and help make relevant information accessible to the organisation and, where applicable, the authorities. It does not take over the controller’s or processor’s decisions about the purposes and means of processing, and it should not be presented as the business’s internal privacy function.
実践的なルール: Treat the representative like a formally designated EU contact for regulatory communications. It must be reachable, properly appointed, and connected to the organisation’s response process.
That distinction matters during a complaint or investigation. If a data subject contacts the representative about a deletion request, the representative should route the request through the company’s established rights-handling workflow. If an authority asks for records, the representative should be able to identify the right internal owner, preserve the exchange, and track the response.
The European Commission’s GDPR text was adopted in 2016 and became applicable on 2018年5月25日, making Article 27 part of the foundational post-2018 governance framework for cross-border digital business. Article 27 does not itself determine whether the GDPR applies. Territorial scope is governed principally by Article 3. If a non-EU controller or processor falls within Article 3(2), Article 27 usually follows unless an exemption is available. Appointment of a representative also does ない, by itself, create an establishment of the controller or processor in the EU.
When Appointment Becomes Mandatory
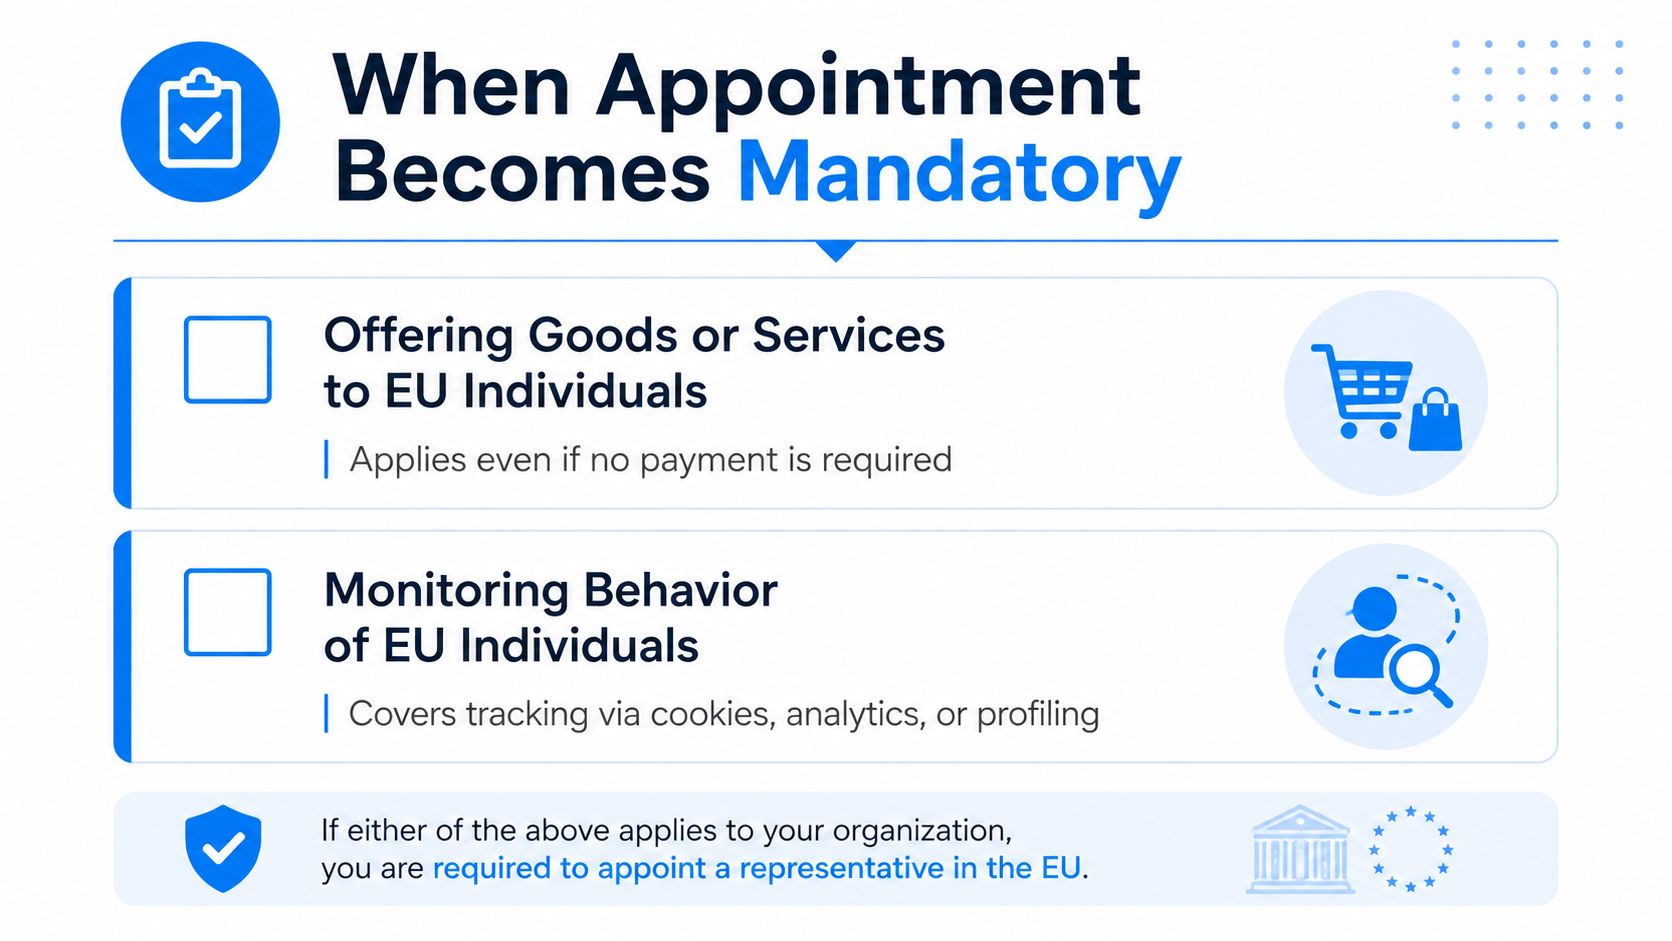
The appointment question starts with two tests. If a non-EU controller or processor is subject to the GDPR because it EU域内の人々に商品やサービスを提供する, 、 または EUにおける人々の行動を監視する, Article 27 may require a representative. The relevant question is not whether the customer paid, whether the company has EU staff, or whether the business calls its activity “global” rather than European.
An Australian online retailer that advertises delivery to Germany is a straightforward example of offering goods or services to EU individuals. A Canadian mobile application that tracks the location of users in France, analyses their activity, or profiles them for targeted engagement may fall within the monitoring trigger. Free services can still qualify, because the offering does not need to involve payment.
Apply the exemption carefully
Article 27 contains a narrow exemption where the processing is only occasional, is unlikely to result in a risk to the rights and freedoms of natural persons, taking into account the nature, context, scope and purposes of the processing, and does not include, on a large scale, processing of special categories of data referred to in Article 9 or personal data relating to criminal convictions and offences referred to in Article 10. Public authorities and bodies are also outside the representative requirement. The exemption should be documented as a reasoned assessment, not treated as a convenient assumption.
Teams often misread “occasional” as “not our main business.” That is not a reliable test. A company whose core product is aimed at EU users may process their data routinely even if Europe represents only part of its commercial activity. Likewise, a business that does not have EU premises can still be subject to the requirement, because the Article 27 analysis may arise once Article 3(2) is engaged.
Use this decision sequence:
-
Identify the organisation’s location. Is the controller or processor established outside the EU?
-
Assess territorial scope. Is the organisation subject to the GDPR under Article 3(2)?
-
Review the trigger. Does it offer goods or services to people in the EU, or monitor their behaviour in the EU?
-
Assess the exemption carefully. Is the processing occasional, unlikely to result in relevant risk, and free from large-scale Article 9 or Article 10 processing?
-
Record the conclusion. Keep the territorial-scope analysis, exemption reasoning, and approval with the privacy governance file.
GDPR Article 27 representative guide
A practical assessment should examine marketing language, currency and delivery options, app availability, cookie and analytics configurations, customer geography, and product functionality. It should also avoid assuming that any use of special-category or criminal-conviction data automatically defeats the exemption. The relevant statutory question is whether such data are processed on a large scale, alongside the other Article 27(2) conditions. If the business cannot explain why the exemption applies, appointing a representative is often the more defensible operational choice.
Core Duties and Responsibilities
The representative’s daily work is mostly about controlled communication. It must remain identifiable to supervisory authorities and data subjects, receive relevant correspondence, and ensure that the appointing organisation can act on it. The role works only when the representative has current company contacts, an agreed escalation route, and access to enough processing information to understand what an inquiry concerns.
Three responsibilities deserve separate treatment.
Handling authority communications
A supervisory authority may send a request about a controller’s or processor’s processing, ask for records, or communicate about a complaint. The representative should log the message, verify its scope, notify the designated internal owner, preserve the original correspondence, and track the organisation’s response. It should not improvise the company’s legal position or answer substantive questions without instructions and appropriate information.
Routing data subject requests
A person in the EU may contact the representative about access, deletion, objection, or another data protection matter. Under Article 27(4), supervisory authorities and data subjects may address the representative, in addition to or instead of the controller or processor, on issues related to processing for the purposes of ensuring compliance with the GDPR. The representative does not decide whether the request is valid or erase the data itself. Instead, it should capture the request accurately, transmit it to the organisation’s rights-response team, monitor the handoff, and retain evidence of the communication.
Weak arrangements fail. A mailbox that nobody monitors creates the appearance of representation without the operational substance. Recommended contractual and operational safeguards should define who acknowledges communications, how identity-verification questions are handled, which team owns the response, and how unresolved requests are escalated.
Maintaining usable records
The representative may be asked to support access to records of processing activities where Article 30 applies. GDPR Article 30 expressly contemplates the representative in the records framework, and the controller or processor and, where applicable, the representative must make the relevant record available to the supervisory authority on request. That requires more than storing a signed appointment letter. The company should maintain an up-to-date processing inventory, controller and processor details, categories of data and individuals, recipient information, retention logic, transfer arrangements, and the representative’s current contact details.
The representative does not become responsible for creating or controlling the organisation’s entire privacy compliance programme. A sound operating model separates formal contact-point duties from privacy advice, security operations, incident response, and business ownership.
A representative should be able to tell an authority who owns the answer, where the supporting record sits, and when the response will be coordinated. If it cannot, the appointment is only paperwork.
Managing Multiple EU Regulatory Frameworks
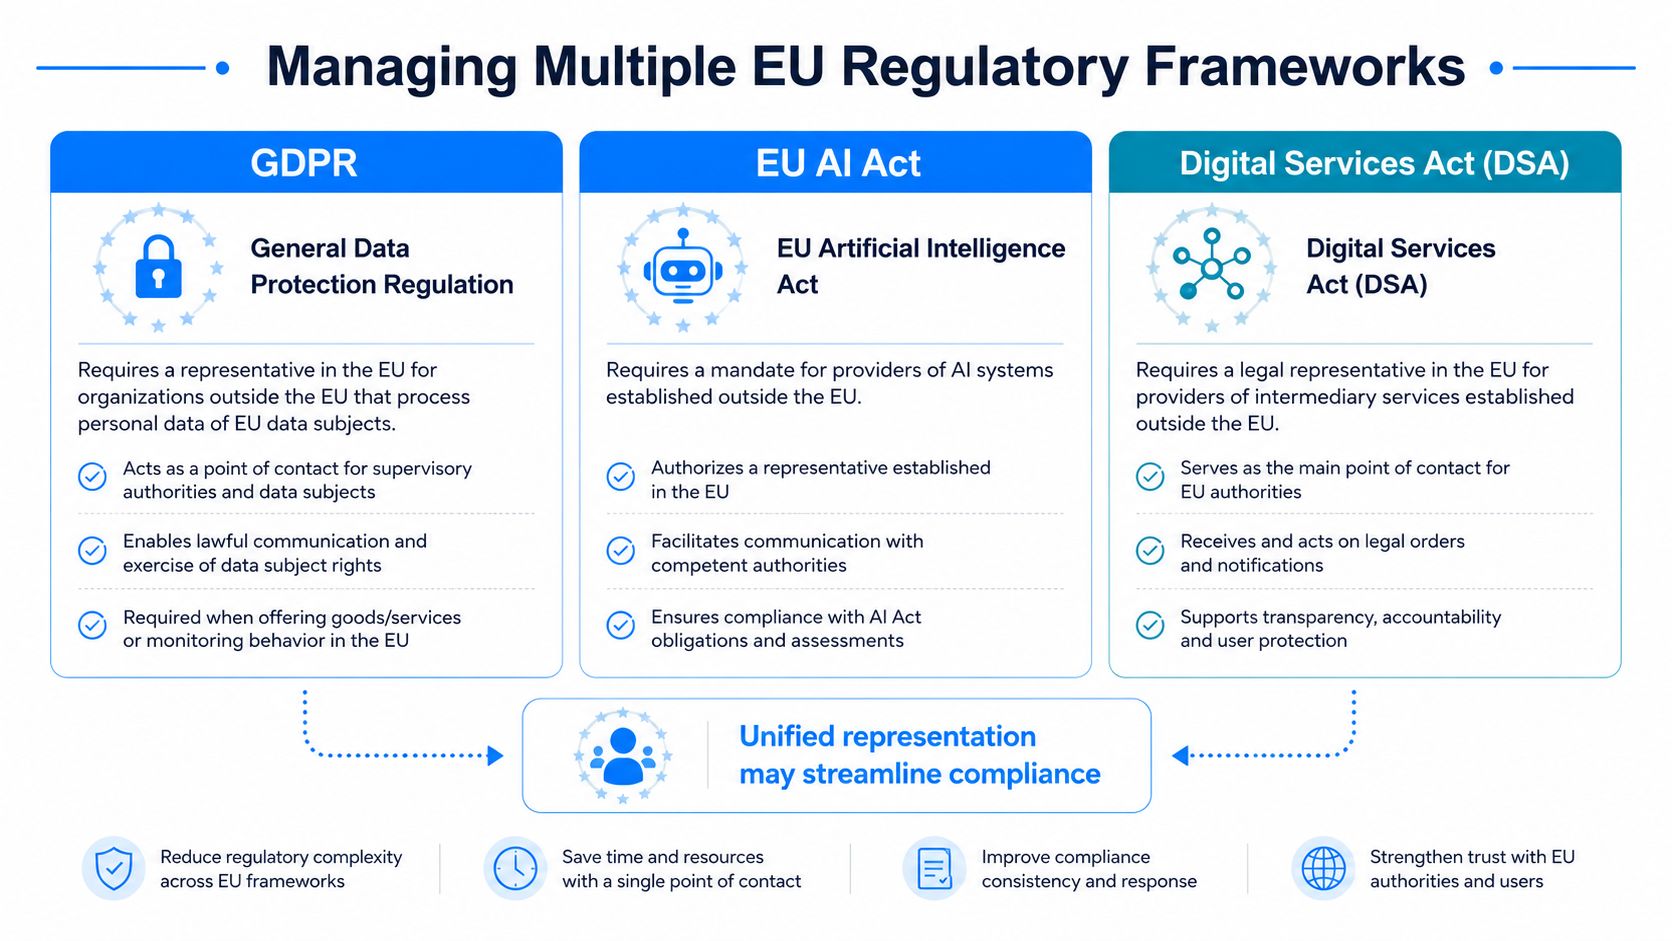
Article 27 is increasingly one part of a wider representation problem. Companies entering European markets may also need to examine representative, authorised representative, or contact-point obligations connected with the EU AI Act, Digital Services Act, Data Act, and NIS2. The exact role, trigger, eligibility criteria, and competent authority differ by framework, so a GDPR Article 27 appointment should not be described as automatically satisfying every other law.
The strategic choice is between fragmentation and consolidation.
| Operating model | What works | Where it creates risk |
|---|---|---|
| Separate representatives | Each provider can specialise in one law and its regulator | Multiple inboxes, inconsistent records, duplicated escalation paths |
| One coordinated mandate | A central intake process can standardise logging, routing, and evidence | Each framework still needs its own valid appointment, scope, and authority |
| Internal EU entity | Local staff may integrate regulatory work with operations | Establishing an entity does not remove the need to map each legal obligation |
A marketplace provider might manage GDPR requests, DSA notices, and Data Act communications through separate teams. A non-EU provider of certain AI systems or models may, depending on its role and the applicable AI Act requirements, also need to assess whether an authorised representative is required. A connected-product manufacturer may need to coordinate GDPR, Data Act, and cybersecurity communications. These examples do not mean one representative is automatically sufficient. They show why the organisation should map obligations before selecting an operating model.
Consolidation needs boundaries
A consolidated mandate can reduce duplicated intake and make it easier to maintain a single register of inbound notices, timestamps, responsible owners, and escalation decisions. It can also give senior compliance teams one view of open regulatory matters rather than requiring them to reconcile several provider reports.
The trade-off is legal precision. Each framework needs its own scope, authority, communication procedure, confidentiality treatment, retention approach, and termination mechanism. A single provider may perform representative or contact-point functions under multiple EU regulatory frameworks where legally permitted, but each appointment must independently satisfy the eligibility, scope, mandate, duties, and other requirements of the relevant legislation.
EU Data Act representative resource
A useful model is one operating channel with framework-specific authority. The provider can accept and log communications centrally, then route each item to the correct legal and operational team under the relevant mandate.
Consolidation makes the most sense when the same organisation has overlapping products, shared privacy operations, and a genuine need for consistent audit trails. Separate appointments may be preferable where a framework requires specialist competence, a regulator expects a distinct contact, or the risks and reporting lines are materially different.
Appointment Process and Mandate Documentation
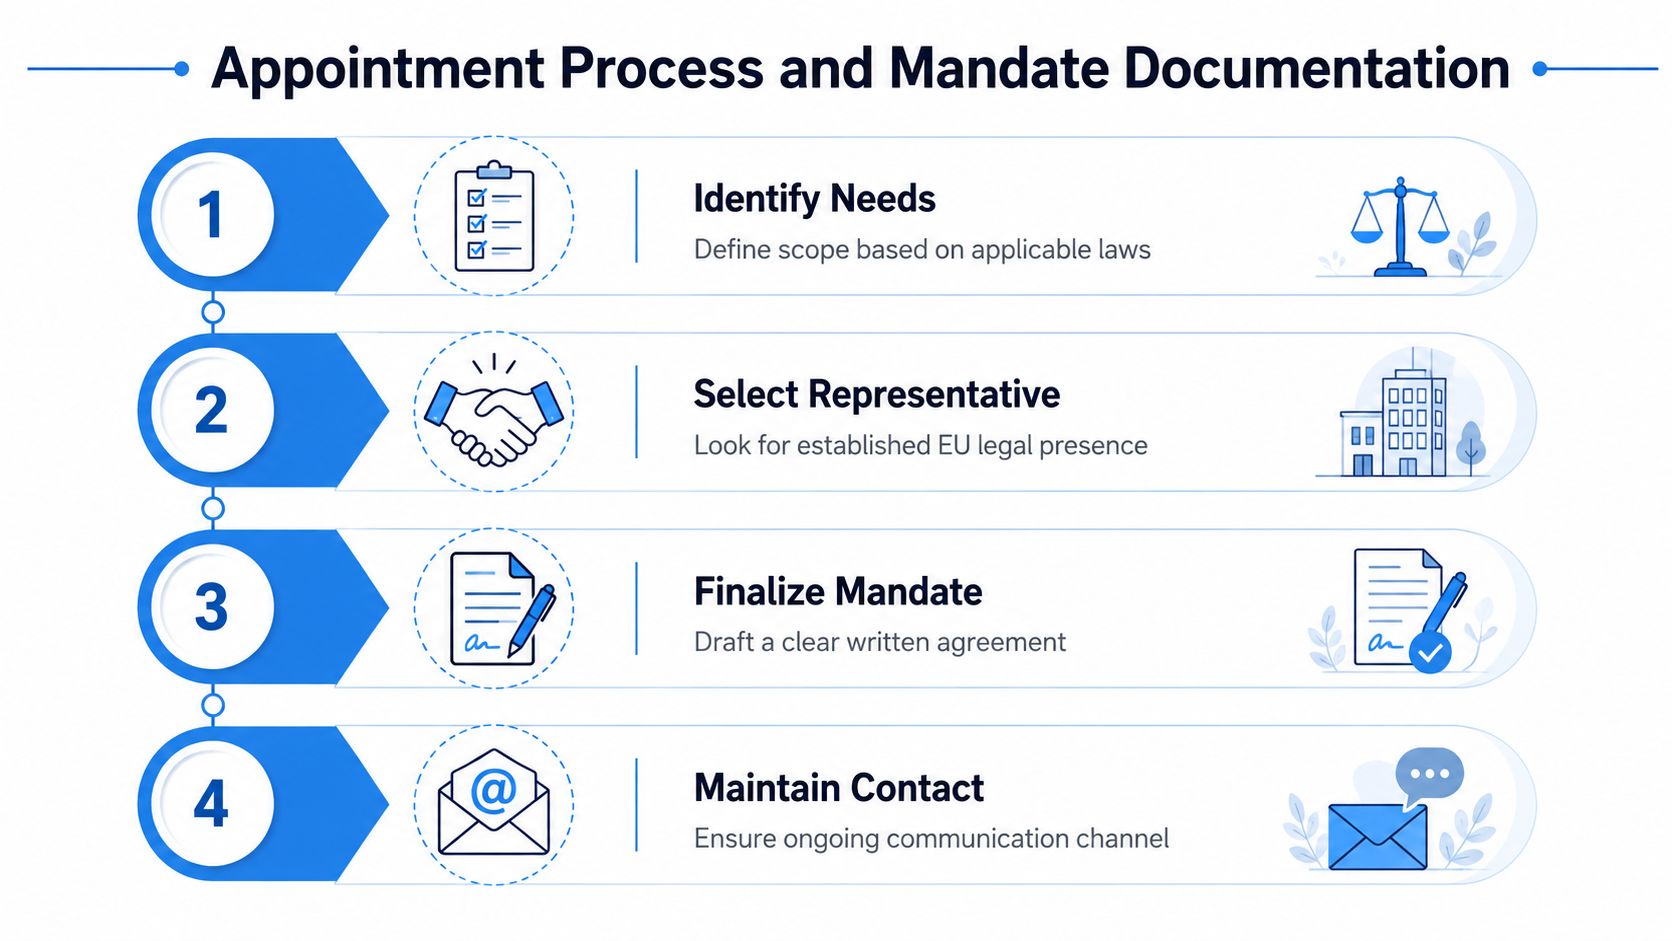
A credible appointment begins with a scope map, not a service-provider shortlist. List each non-EU legal entity, the products reaching EU individuals, the relevant processing activities, the Member States where affected data subjects are located, and the frameworks that may require an in-market contact. This prevents a company from appointing someone for one brand while leaving another controller or processor outside the mandate.
Select for operational readiness
The representative must be established in an appropriate EU Member State, and the organisation should test whether the proposed provider can communicate effectively with the relevant authorities and data subjects. Industry familiarity matters when a provider needs to understand a SaaS platform, advertising technology, connected product, health service, or AI system quickly.
Ask practical questions:
-
Who monitors inbound communications? Get the named function, coverage process, and escalation owner in writing.
-
What gets logged? Confirm that notices, requests, timestamps, attachments, forwarding actions, and resolution status are retained.
-
How is authority scope controlled? The provider should distinguish forwarding and coordination from making the company’s compliance decisions.
-
What liability arrangements apply? Review insurance, exclusions, subcontractors, confidentiality, and cooperation duties.
-
What happens after termination? The agreement should explain handover, notice updates, record retention, and regulator communication.
These are recommended diligence and contracting points, not a complete list of statutory Article 27 requirements. They help turn the appointment into an operationally usable arrangement.
Write a mandate that can withstand scrutiny
GDPR Article 27 requires the designation to be 書面で. The mandate should identify the appointing entity, representative, applicable processing scope, authority to receive communications, data subject contact arrangements, escalation procedures, confidentiality expectations, liability allocation, cooperation duties, and termination terms. It should also state which additional frameworks are included, if any, rather than relying on a broad label such as “European compliance.” Some of these points are statutory minimums, while others are recommended contractual safeguards that help the arrangement function in practice.
Update the privacy notice and other relevant public-facing information with the representative’s identifying details where transparency obligations under Articles 13 and 14 GDPR apply. Keep the signed mandate, corporate authority evidence, processing inventory, scope assessment, exemption analysis if relevant, and change log together. Revisit the records when products, customer regions, tracking tools, legal entities, or regulatory duties change.
EU AI Act authorised representative service
Use a short implementation sequence: approve the scope, complete due diligence, sign the mandate, publish contact details, test the intake route, brief customer support and privacy teams, then schedule periodic checks. For organisations with AI products, any separate authorised representative requirement should be evaluated independently from the GDPR mandate, even where one operating model is intended.
Enforcement Risks and Compliance Consequences
Failure to designate an Article 27 representative is treated as an Article 83(4) infringement. Under Article 83(4)(a) GDPR, infringements of the obligations of the controller and the processor pursuant to, among other provisions, Article 27 are subject to administrative fines of up to €10 million or, in the case of an undertaking, up to 2% of the total worldwide annual turnover of the preceding financial year, whichever is higher.
That ceiling should not be treated as a prediction of an outcome. It does show why the appointment belongs in the organisation’s risk register. A missing representative can also make ordinary regulatory events harder to manage. A complaint may arrive through an unexpected channel, a breach notification may lack a clear recipient, and an authority’s request may sit unanswered while internal teams determine who owns it.
guidance on Article 27 enforcement exposure
guidance on Article 27 enforcement exposure
guidance on Article 27 enforcement exposure
How gaps become visible
Supervisory authorities and data subjects can expose the gap through complaints, investigations, or requests for information. Cross-border cooperation can also make an inconsistent contact structure more apparent, especially when a company operates several products or legal entities under one brand.
管理者または処理者は、GDPRの実質的な遵守、処理に関する決定、および関連活動の法的根拠全般について引き続き責任を負います。代理人は、委任およびその役割に伴う義務に関して、独自の法的役割と潜在的なリスクを負い、これにより商業関係が変化します。したがって、プロバイダーは明確な委任、適切な手順、および明確なエスカレーションモデルを持つ必要があります。代理人を任命しても、管理者または処理者のGDPR上の責任が代理人に移るわけではありません。.
リスク管理の観点から: 担当者は、違法な処理行為を修復することはできません。しかし、基本的な連絡の不備が、ガバナンスプログラムが不完全であることを示す最初の証拠となることを防ぐことはできます。.
実務的な対応は単純明快です。トリガーとなる事象を確認し、例外事項を文書化し、関連するEU関連活動を開始する前に代理人を任命し、正確な詳細情報を公開し、通信経路をテストし、プロセスが機能している証拠を保全します。このアプローチは、当局やデータ主体が欠落したリンクを発見するのを待つよりも効果的です。.
EU市場戦略に代理店業務を組み込む
担当者の選定は、製品発売、プライバシーに関する通知、データ処理記録、権利対応手順、インシデント管理、およびデータ保護責任者(DPO)による評価と並行して計画されるべきです。発売後に担当者を任命すると、カスタマーサポート、法務、セキュリティチームが連携した対応を必要とするコミュニケーションに備えることができなくなる可能性があります。.
市場参入計画は、次の4つの質問に答えるべきである。
-
サービスの提供または処理目的の決定は、どの主体が行っているのか?
-
どのようなEU市民や行動が対象とされ、監視されているのか?
-
どのような法的枠組みが、当該製品に関するコンタクトポイント義務を規定しているのか?
-
通知や要求が届いた後、それぞれの応答の所有権は誰にあるのでしょうか?
最も優れた運用モデルは、顧客対応をインフラストラクチャとして捉えます。これにより、顧客や関係当局は組織への明確なアクセス経路を得ることができ、文書化された引き継ぎプロセスが確立され、新たな市場開拓の意思決定を毎回ゼロから始める必要なく、事業拡大が可能になります。また、各チームが対応の承認者、記録の保持者、広報担当者の情報更新者を明確にする必要があるため、内部の責任体制も明確になります。.
予算には、任命料だけでなく、業務範囲の見直し、通知の更新、受付テスト、記録管理、職員研修、フレームワークのマッピング、定期的な業務範囲チェックなども含めるべきです。通信状況の監視や監査証跡の保存ができない低コストの任命は、削減できる業務量よりも、かえって業務負担を増やす可能性があります。.
欧州のデジタル規制が発展していく中で、企業は孤立したコンプライアンス体制を構築することを避けるべきです。GDPR、AI、プラットフォーム、データアクセス、サイバーセキュリティといった義務が互換性のあるものであるかのように装うことなく、枠組みに特化した法的評価と、統制された集中型コミュニケーションモデルを組み合わせることで、統合を促進することができます。.
Dilicheck Repは、GDPR第27条、EU AI法、デジタルサービス法、データ法、NIS2コンタクトポイントサービスを含む、EUおよび英国の正式な規制代理業務を提供し、委任文書の作成と、当局およびデータ主体とのコミュニケーションの構造化された処理を行います。代理業務の範囲と運用モデルについては、 ディリチェック担当者 次回のEU市場参入前に。.
免責事項: 本ガイドは一般的な情報提供のみを目的としており、法的助言を構成するものではありません。EUのデータ保護およびその他の規制要件の適用は、各組織の具体的な状況によって異なります。本情報に依拠したり、法令遵守に関する決定を下したりする前に、必要に応じて適切な法的助言を得てください。.
最終更新日:2026年8月
開示:この記事は、プライバシー専門家がAIの支援を受けて作成しました。.